That's not very sneakry.
Today we saw the biggest Github actions attack ever! What a time to be a alive. And there's plenty of excellent coverage out there of the malware, campaign, and its impact. You can read it from these reputable sources.
WFX and GhostAction: Tracing the Links Between Two GitHub Attacks
wfx: GitHub Actions Credential Stealer Hits 8,000 Repos
But we don't care about that, what we care about is the who, and the how.
The shortest version is this. The WFX operator runs a commercial Russian-language VPN service called Sneakry VPN, sold through Telegram.
The long version is this.
Starting earlier this afternoon, stolen GitHub tokens were used to a push a secret stealer into repositories via 1 of 3 methods.
| Method | Commit message | Observed | Exfil endpoint |
|---|---|---|---|
| Inject into existing workflow | ci: refresh build cache | 28,593 commits since Nov 10 | 194.150.166.244:8080/exfil |
| Hidden script + postinstall | chore: add ci helper | 4,008 commits since Nov 10 | 18.143.168.96:8080/exfil |
| New workflow file | varies (build-audit-*.yml) | smaller volume, found via code search | 194.150.166.244:8080/exfil |
The attacker opens probe PRs titled "docs: dependency audit notes" from a branch called wfx-docs
After injection, the attacker pushes ci: restore or ci: cleanup commits and deletes the Actions run logs. In one victim's timeline the cleanup commit landed one minute after the payload commit.
The payload itself targets:
- GitHub Actions secrets and variables
- Runner process memory
- Cloud CLI credentials (AWS, GCP, Azure)
- SSH and GPG keys
- Package manager tokens (.npmrc, .pypirc)
- .env files and Terraform state
- AI provider keys (OpenAI, Anthropic, Google, Mistral, Groq, and ~50 others)
- GitHub OIDC tokens, exchanged for AWS/GCP/Azure sessions
For a full breakdown of the payload, read Ossprey Security's analysis. We're moving on.
The Infrastructure
Two exfil endpoints were used across the campaign:
| IP | Port | Provider | Location | Used by |
|---|---|---|---|---|
| 194.150.166.244 | 8080 | Regxa (AS215311) | London, UK | Workflow variants (injection + new file) |
| 18.143.168.96 | 8080 | AWS EC2 (AS16509) | Singapore | Postinstall variant |
We can't get anything further from the AWS IP, the server is now down and since then the IP has likely been rotated back into the pool, so we'll have to leave that to AWS to investigate.
That 194.150 IP is interesting though. It was the C2 used by 2 of the 3 attack methods. By the time I got around to checking it, the service running on port 8080 had been shutdown but some things remained. The most important of those was on port 80.
An Ubuntu server running nginx/1.24.0 serving a redirect to avalon-n.sneakry.com
Ok, that's strange. And it gets even better.
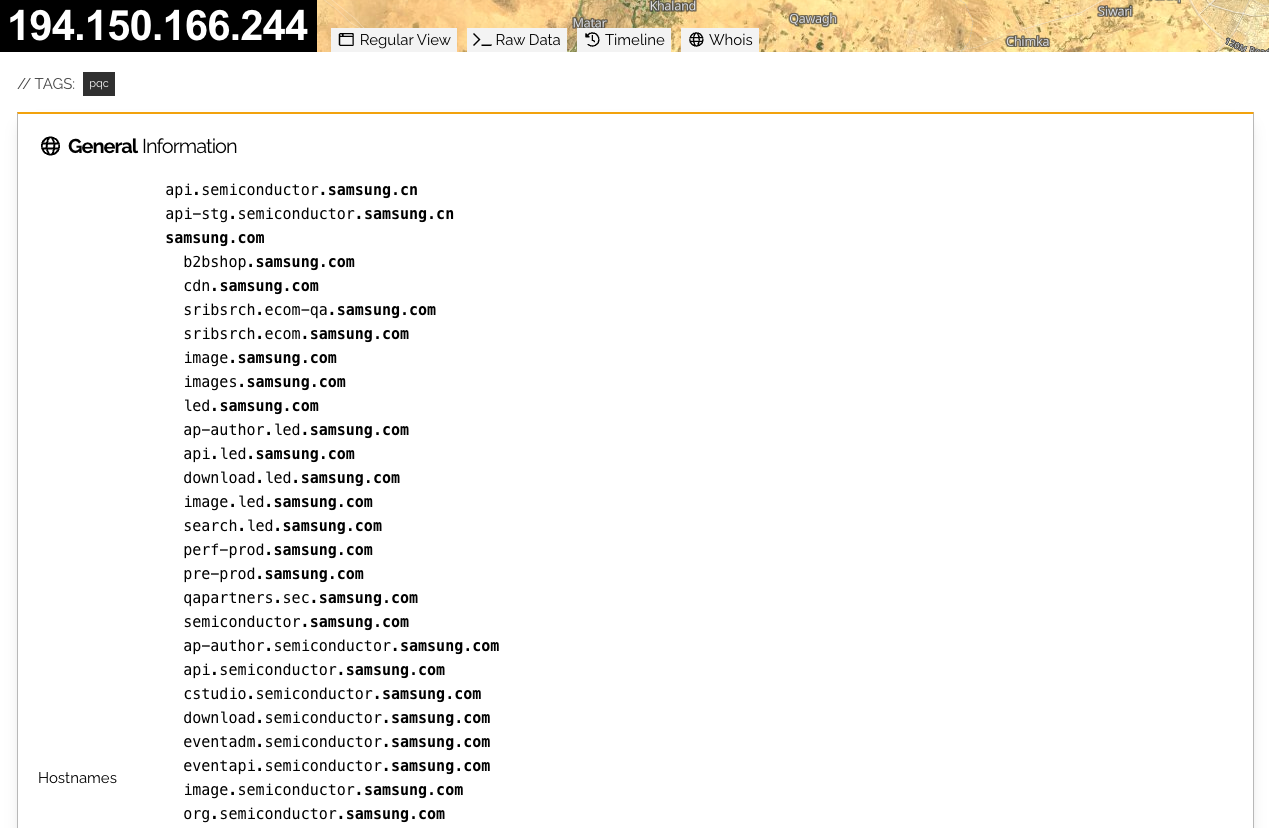
194.150.166.244 Up until last week, this IP used to belong to Samsung's Akamai CDN infrastructure. Akamai Ghost servers are the edge caching proxies that deliver Samsung's web content, it appears that they recently moved away from this IP range.
Once they did, the WFX attack operator was able to rent it from Regxa Company (AS215311), a small privacy-friendly hosting provider based in London.
This is a sidenote, but it's interesting because commercial IP info services still associated this IP with Samsung services, and it's likely a nice trust score comes along with that.
Sneakry and the proxy network
Port 80 on the exfil box redirects to avalon-n.sneakry.com. That domain is part of a distributed proxy/relay network the operator has been running since at least July 2025.
Certificates transparency logs show 142 TLS certificates affiliated to sneakry.com and its subdomains. Of the 30 subdomains seen, 10 were resolvable at the time of writing.
| Subdomain | IP | Provider | Location |
|---|---|---|---|
| sneakry.com (origin) | 206.206.77.121 | Regxa AS215311 | Singapore |
| avalon-n.sneakry.com | Cloudflare | Cloudflare | — |
| edge.sneakry.com | Cloudflare | Cloudflare | — |
| proxy/orion.sneakry.com | 150.251.112.120 | Regxa AS215311 | Warsaw, Poland |
| fire.sneakry.com | 194.150.166.244 | Regxa AS215311 | London, UK |
| fallout.sneakry.com | 145.223.69.42 | Regxa AS215311 | Roubaix, France |
| eleven/five/mini.sneakry.com | 206.206.77.121 | Regxa AS215311 | Singapore |
| hy2.sneakry.com | 46.16.34.8 | AlexHost (AS200019) | Las Vegas (Moldova reg.) |
| web.sneakry.com | 82.194.165.212 | RTComm.RU (AS8920) | Vladivostok, Russia |
| ig.sneakry.com | 185.216.19.98 | Mega Tec (AS205500) | Vladivostok, Russia |
Every primary node is on Regxa (AS215311), the same hosting provider as the exfil box. fire.sneakry.com resolves to 194.150.166.244 — the wfx exfil server itself.
We later signed up for the VPN's own trial and pulled the customer configs: the exits paying users get are orion (Warsaw), fallout (Roubaix), avalon-n (Cloudflare-fronted) and atlas (Frankfurt).
All of these were branded into the same sneakry.com family, the first two on the same Regxa account as the exfil box. fire isn't an exit node. It's the operator's own machine, receiving stolen credentials from thousands of CI runners one hop away from where the customers browse.
The relay nodes use additional providers:
- AlexHost (Moldova-registered, Las Vegas IP) for the Hysteria2 censorship-evasion proxy — a known bulletproof hosting provider
- RTComm.RU and Mega Tec (Vladivostok, Russia) for additional web nodes
Sneakry as a VPN
web.sneakry.com serves a Russian-language Telegram Mini App for a commercial VPN service called Sneakry VPN.
Добро пожаловать в Sneakry Быстрый доступ без ограничений на всех устройствах ⭐ Telegram Stars — Мгновенно, прямо в Telegram
Translation: "Welcome to Sneakry. Fast access without restrictions on all devices. Telegram Stars — Instantly, right in Telegram."
The service is a mini app that runs inside Telegram, is paid with Telegram Stars (Telegram's in-app currency), and targets Russian-speaking users.
Payment is processed through @TrustStarsBot, a Russian-language Telegram Stars purchasing service with support (@TrustStarsHelp), reviews (@TrustStarsOtz), and news (@TrustStarsNews) channels.
The Telegram Exfil Evolution
The campaign shows a clear evolution in exfiltration methods:
| Variant | Exfil method | Infrastructure needed |
|---|---|---|
| Early (workflow injection) | HTTP POST to 194.150.166.244:8080 | Yes — dedicated exfil server |
| Late (hidden script/postinstall) | HTTP POST to 18.143.168.96:8080 | Yes — AWS EC2 instance |
| Newest (hidden script v2) | Telegram Bot API | No — Telegram's infrastructure |
The newest .ci scripts found in victim repositories contain five active Telegram bot tokens used as an exfil worker pool.
| Bot | Username | EGO status |
|---|---|---|
| Worker1 (8708988906) | @worker1qwevqqweqweqwevqw_bot | administrator |
| Worker2 (9196217635) | @Worker2qweqwcvqweqe_bot | kicked |
| Worker3 (9180059428) | @worker3qweqcwecqwecqwecQW_bot | administrator |
| Worker4 (8902935164) | @worker4qwecqwecqwec_bot | administrator |
| Worker5 (8876515636) | @Worker5qweqwceqwecqweQWce_bot | administrator |
As investigation was on-going it was noticed that worker2 had been kicked from the group. This essentially means that functionally some percentage of data is being lost before being exfilled if it resolves to worker2.
The bots send stolen data to a private Telegram supergroup called EGO (ID -1004340163187) using the sendDocument API method. The channel has no public username, no description, and cannot be joined without an invite link.
One last tell in the newer scripts: the HTTP callback is still there — but set to http://127.0.0.1:1/x, a dead localhost port. The stealer's whole HTTP exfil path now terminates in a void while Telegram does the real work.
The channel has five members. Four are the bot administrators. The fifth — the channel creator, is the operator's personal account:
- Telegram User ID: 7349133718
- Display name: "NG PANEL 😜"
- Username: hidden via privacy settings
- Profile photo: custom "NG" logo (black background, white stylized letters)
This is a significant operational upgrade. Telegram hosts the exfil endpoint. Takedown requires Telegram's cooperation, not a server seizure.
The GhostAction connection
The wfx campaign is not the first time this technique has been used. In October 2026, the GhostAction campaign used the same delivery method.
| Indicator | GhostAction (October) | wfx (November) |
|---|---|---|
| C2/exfil | 193.32.204.199 (Madina IT, Helsinki) | 194.150.166.244 (Regxa, London) + 18.143.168.96 (AWS, Singapore) |
| Workflow names | security-audit.yml, github_actions_security.yml | build-audit-*.yml, build.yml (injected) |
| Commit messages | "Add security audit workflow" | "ci: refresh build cache", "chore: add ci helper" |
| Technique | Single workflow injection | Injection + hidden script + postinstall + Telegram exfil |
| Capabilities | Secrets theft | + OIDC cloud exchange, AWS/Entra persistence, status forgery |
| Scale | Smaller | 4,837 accounts / 61,764 repos probed |
We did not see any infrastructure re-use between the WFX campaign and GhostAction.
What was re-used between the waves is the access. We observed hijacked accounts that were hit in both waves, and found continuity with 1 victim:
aman-reso/fl_audio_book (Gulshan Raj):
- Oct 8: "Add security audit workflow" — GhostAction injects using the
security-audit.ymlfilename (a GhostAction IOC) - Nov 10: "ci: refresh build cache" — wfx updates the same file with the wfx payload (exfil to 18.143.168.96)
Interestingly we found that in this case the same repo, and the same file was replaced in place, from the GhostAction to the WFX malware.
To me this indicates that we're looking at the same actor who's come back with a better toolkit.
The victims
GitHub commit search identified 28,593 injection commits and 4,008 hidden-script commits matching wfx IOC patterns since November 10. We paginated through 2,000 of them (a 4% sample), identifying 1,384 unique victim repositories across 556 account owners.
The estimated total is ~22,000–32,000 unique victim repositories.
The attack targeted all major development ecosystems. JavaScript/Node, Go, Python, Rust, cloud infrastructure — across Indian, Indonesian, Vietnamese, Russian, European, American, and Middle Eastern developers.
IOCs summary
| Type | Indicator |
|---|---|
| Exfil IP | 194.150.166.244 |
| Exfil IP | 18.143.168.96 |
| GhostAction C2 | 193.32.204.199 |
| Proxy network | sneakry.com (origin: 206.206.77.121) |
| Relay node | 150.251.112.120 (proxy/orion) |
| Exfil node | 145.223.69.42 (fallout) |
| Hysteria2 proxy | 46.16.34.8 (hy2) |
| Web node | 82.194.165.212 (web) |
| IG node | 185.216.19.98 (ig) |
| Telegram bot | @worker1qwevqqweqweqwevqw_bot |
| Telegram bot | @Worker2qweqwcvqweqe_bot |
| Telegram bot | @worker3qweqcwecqwecqwecQW_bot |
| Telegram bot | @worker4qwecqwecqwec_bot |
| Telegram bot | @Worker5qweqwceqwecqweQWce_bot |
| Telegram channel | EGO supergroup (ID -1004340163187) |
| VPN service | Sneakry VPN (t.me/SneakryVPN) |
| Attacker account | wfx-docs (removed, 404) |
| Attacker account | wdio-bot (still active) |
| Attacker Telegram | ID 7349133718 ("NG PANEL 😜") |
| Stealer hash | 7f3a7961a50c23ddbb048828845120dd0605a4c7617b1cdfe489d84bc7d33fa9 |
| Stealer hash variant | 89695abb392d5cfd4972672961e644bb46baa98aa1ed7173c2a2816c762735cf |
| Marker | <!--WFX-BEGIN--> |
| Marker | #ghc2 |
| Staging name | wfx-loot-* |
Thanks for reading, this article was a chance for me to dig into some infrastructure. Hopefully you found it interesting. As always leave a comment wherever you found this and check out some more posts on research.veryserious.systems.